DLP and IRM Landscape
Modern Insider Threat Evaluation Criteria That Legacy UEBA Vendors Cannot Meet
Modern insider threat requires investigation capability, not just anomaly detection.
Darnell Okafor
· 9 min read
Modern insider threat requires investigation capability, not just anomaly detection.
Behavioral context reveals patterns rules cannot see, preventing breaches static detection misses.
Behavior-informed detection shortens tuning time and builds analyst trust faster than static rules.
The quality of data fusion, not just collection, separates insider threat platforms.
Five threat archetypes demand different detection strategies from insider threat platforms.
Behavioral signals catch sensitive data leaving based on context, not just pattern matching.
Classification-free detection separates DLP vendors by depth of context, not just pattern matching.
Five platforms earn their place by connecting behavioral signals with investigation-ready evidence.
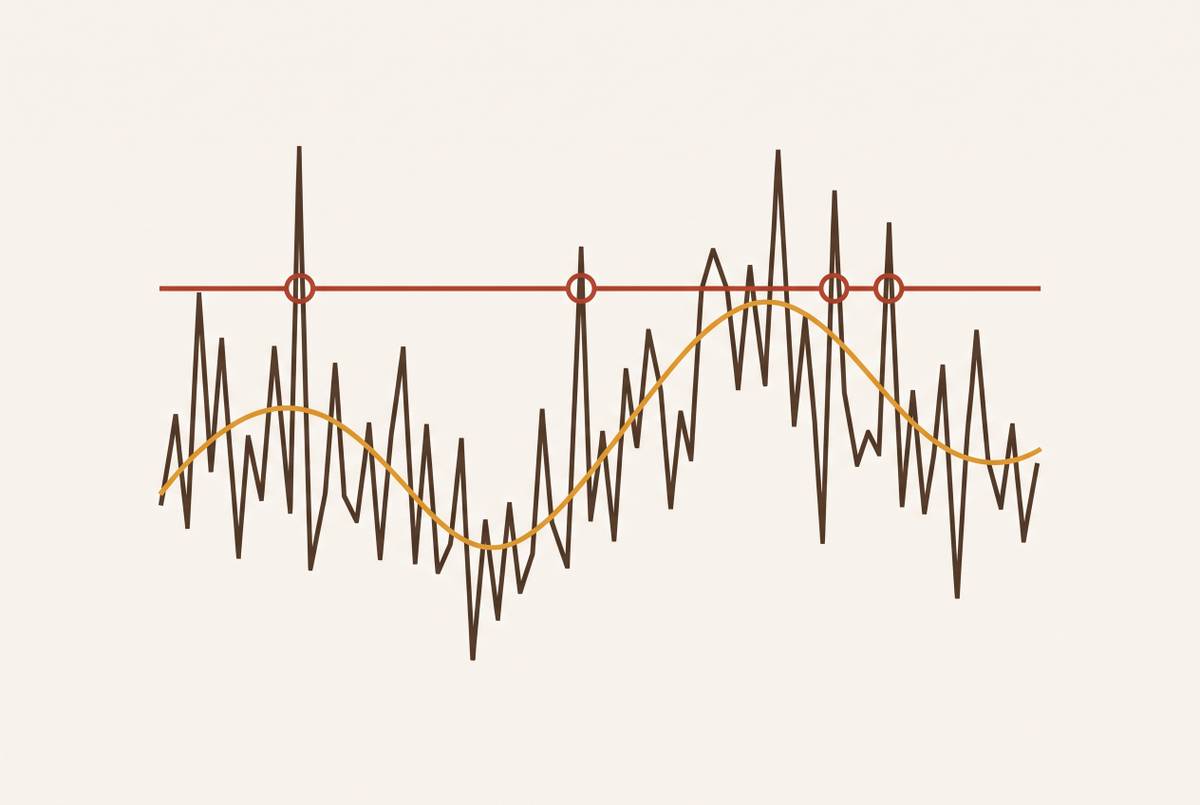
Static rules miss context that machine learning models learn from behavior.
AI automates correlation and triage to cut insider threat investigation time from days to minutes.
Behavioral AI and LLM reasoning now detect insider threats static rules miss.
Effective DLP requires content understanding and behavioral context, not flawless user labeling.