AI-Native Insider Threat Platforms Replacing Rule-Based Detection in the Modern SOC
AI learns what normal looks like for each user, catching insider threats rules miss.
Rule-based insider threat detection is failing for reasons that have little to do with misconfigured policies or alert fatigue. The failure is architectural. The next generation of insider threat platforms replaces that question with a different one entirely.
Why rule-based detection fails insider risk architecturally — not just operationally
A rule does exactly what it is written to do, and nothing more. It asks whether something happened: a file moved, a volume threshold crossed, a keyword matched. A rule catches the event. It cannot catch the story the event belongs to. <sentence>Signature-based and rule-based detection needs an exact match against a known template, so it is structurally blind to anything that does not fit, including fileless attacks and living-off-the-land techniques that use legitimate tools.>
The insider threat problem is precisely this mismatch. Insiders use authorized credentials, authorized systems, and authorized workflows. Nothing about any individual action is anomalous. Only the pattern across time and identity reveals the risk, and a rule has no way to assemble that pattern. AI-driven detection distinguishes itself by asking a fundamentally different question: instead of testing whether an action matches a rule, it learns what normal looks like for a specific user and entity, then flags deviations from that norm.
The Intel case illustrates the gap in operational terms. A DLP rule blocked one exfiltration attempt by former employee Jinfeng Luo, who then switched to a personal NAS device and completed the exfiltration through a different channel. Blocking one channel left every other channel open, because the rule had no model of the person who was acting, only of the channel they happened to use that day.
Three structural blind spots recur throughout this analysis, and each deserves explicit naming. The first is the person: a rule has no model of who is acting. It treats the same action identically whether performed by a new hire, a departing executive, or a contractor with a history of anomalous access. The second is the data's meaning. Most crown-jewel intellectual property carries no classification label. It is sensitive because of what it means to the business, not because it matches a regex, so a rule that fires on labels silently misses the data that was never labeled. The third is the pattern. What looks like a benign file move on day one is evidence when viewed against thirty days of after-hours access, unusual queries, and cloud sync activity.
How the insider threat surface has expanded to make rule-based coverage structurally thinner over time
The architectural gap is widening, not holding steady. The attack surface for insider risk has grown faster than rule libraries can track. SaaS sprawl, cloud data gravity, remote work, and widespread AI tool adoption have multiplied the channels through which sensitive data moves, and each new channel requires new rules that arrive only after exposure has already occurred.
Shadow AI is the sharpest current example of this expansion. Employees independently adopt AI tools and upload proprietary data into chatbots, sync transcripts to unsecured third-party platforms. These behaviors are now widespread, not edge cases. A static rule written for a known sanctioned tool has no visibility into an unsanctioned AI destination the security team has not yet identified. Candor's position on shadow AI is that it cannot be solved through visibility alone or by banning AI. Controls need to depend on the data, the destination, account ownership, and context, with intervention before sensitive data leaves.
The insider threat population has expanded beyond the malicious employee. The Rippling case demonstrates the consequence: an alleged competitor-planted spy operated inside the organization for four months, accessing Slack, Salesforce, Google Drive, and Gong using valid employee credentials but far outside his authorized role scope, exfiltrating customer data and pricing information. The Coinbase case in May 2025 followed the same shape: external attackers bribed support agents who used legitimate access to exfiltrate customer data on tens of thousands of users. Authorized credentials, authorized actions, no rule to fire.
The recruitment threat adds an external dimension that purely behavioral rules miss. Flashpoint tracked 91,321 instances of insider recruiting, advertising, and threat actor discussions in 2025. Organizations remain permanently behind because the rule-writing cycle is slower than the adoption cycle.
What happens inside the SOC when rules generate more signal than analysts can act on
The operational result of rule-based detection at scale is not protection. It is alert overload that forces analysts to triage quantity rather than investigate quality, and the most sophisticated insider threats succeed precisely because they blend into the noise. Security teams have admitted ignoring alerts that later proved critical, not because analysts are careless but because volume makes selective attention the only rational strategy.
Mean time to investigation is the operational gap that threats exploit. A platform that surfaces the right alert but leaves the analyst to reconstruct context from scratch has not solved the problem. It has moved it.
The diagnosis completes itself here. If the failure were merely operational, a tuning exercise might suffice: better thresholds, fewer alerts, more analysts. But the failure is architectural, built into the design unit of the rule itself. The solution must therefore be architectural as well.
How AI-native platforms close the architectural gap rule-based systems leave open
AI-native platforms close the architectural gap because they are built around the right question. They do not ask whether an action matches a rule. They ask whether this is what this person would normally do with this data, given everything known about them and their context. Answering that question requires modeling the person, the data, and the pattern simultaneously.
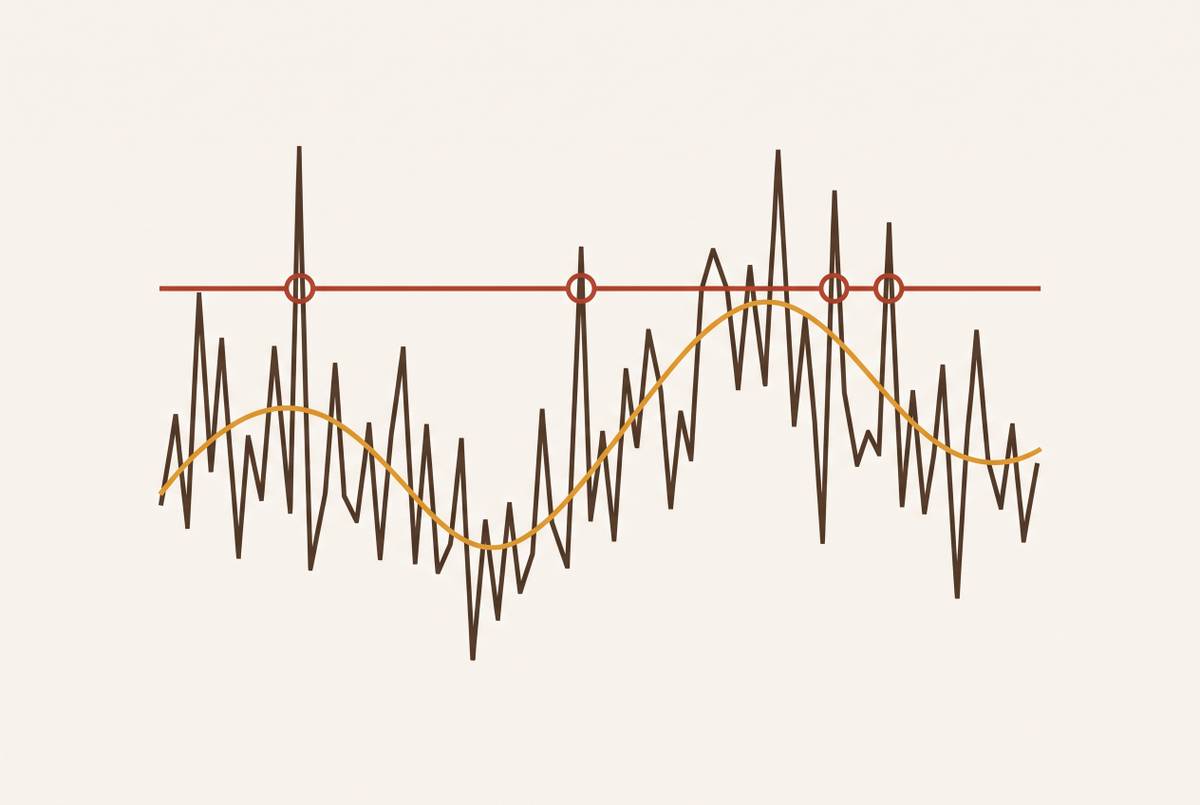
Behavioral baselining is the foundational mechanism. The system learns what normal looks like for each user and entity across their full activity timeline, so a deviation from that baseline surfaces as a signal even when every individual action is individually authorized. Supervised models learn known threat patterns, unsupervised models identify anomalies that no existing rule covers, and together they catch both known archetypes and novel behavior. This directly addresses blind spot one, the person: the system has a model of who is acting and what their normal looks like, not just what action was taken.
Understanding data meaning, not just data movement, addresses blind spot two. AI-native platforms assess what information means to the business, not just whether it matches a label or a regex. Crown-jewel IP without a classification label is invisible to rule-based DLP. A platform that understands content, destination, role, and context can assess risk even when the file has never been tagged. Content, destination, identity, role, and surrounding behavior belong in the same decision.
Pattern assembly across the full user timeline addresses blind spot three. Rather than resolving each alert in isolation, AI-native platforms correlate events across time and systems into a single behavioral narrative. The risk lives in the behavioral pattern across the entire user timeline.
The Yahoo case illustrates what the behavioral layer should catch. In 2022, senior research scientist Qian Sang exfiltrated hundreds of thousands of pages of confidential AdLearn source code, backend architecture information, secret algorithms, and other intellectual property. An automated system correlating data volume, access patterns, and departure timing across the user's timeline should have flagged the pattern before exfiltration completed. Agentic architectures extend this further. Agentic SOC platforms deploy autonomous agents that continuously monitor telemetry streams using unsupervised learning, correlate relationships between disparate events using graph-based analysis, and execute response actions based on real-time risk assessment, compressing the time between detection and response to minutes rather than days.
Why explainability and auditability are architectural requirements, not optional features
The strongest objection to replacing rules with AI is epistemological, not technical. A rule is auditable by design. The objection is legitimate and cannot be dismissed. AI-based threat detection also carries a higher risk of false positives if models are poorly tuned or training data is low quality, and the discipline of data quality and model governance cannot be skipped.
The answer is not to abandon AI-native detection. It is to build explainability and auditability into the architecture from the start. The goal is not a black box that fires alerts but a system that assembles and surfaces the full story behind each finding. When the platform delivers a behavioral narrative, this user, these systems, this sequence of events, over this timeline, an analyst can evaluate, validate, and act on the finding without reconstructing the reasoning from scratch.
Static rules are not obsolete for all purposes. They handle structured, regulated data with known patterns reliably, and nothing replaces them for that job. Modern stacks integrate both layers: deterministic rules for known, structured scenarios, and behavioral AI for the broad space of unstructured, unlabeled, and novel risk that rules cannot reach. New global cybersecurity frameworks increasingly expect continuous monitoring, rapid incident reporting, and automated resilience, and the outputs of that automation must be defensible in audit and legal contexts.
What MTTI reduction looks like in practice when the investigation arrives pre-assembled
The most direct operational benefit of AI-native insider risk detection is not catching more events. It is delivering the investigation context alongside the alert, so the analyst's job shifts from reconstructing what happened to evaluating and acting on a story the platform has already assembled. An investigation workflow measured in days means the data is long gone before the analyst begins.
Pre-assembled investigation changes what the analyst receives. Investigation AI provides conversational interfaces enabling natural language threat hunting, removing the dependency on SQL expertise or deep platform familiarity for initial investigation steps. For insider risk specifically, this means the behavioral timeline, what the user accessed, when, from where, how it compares to their baseline, and what data was involved, arrives with the alert rather than requiring the analyst to pull it from five separate systems.
The design philosophy behind Candor's approach is that AI should investigate candidate events before they become human alerts. The AI layer handles the investigative groundwork, so the human decision point is evaluation and action rather than reconstruction. The operational viability of this approach shows in the Assala Energy case, where an AI SOC deployment cut alert triage time from 25 minutes to under 5 minutes for common scenarios, with a significant reduction in false positives requiring manual review. The compression in analyst time is achievable at operational scale, not just in benchmarks.
How AI-native platforms integrate with existing security stacks rather than replacing them
The prevailing modernization pattern is integration, not wholesale replacement. <sentence>AI-native insider risk platforms extend and improve existing security investments rather than requiring organizations to start over, and that is the critical adoption advantage for lean security teams already managing complex toolchains.> Modern DLP stacks are increasingly assembled from interoperable component layers rather than a single monolith, moving beyond legacy perimeter-based enforcement toward a discovery-led data control plane. Graduated enforcement is a design requirement for insider risk that binary block-or-allow rules cannot support. The distinction matters because the goal of insider risk management is not maximum friction but accurate intervention. An overly aggressive block policy on a negligent user creates friction without reducing risk, while a targeted behavioral response addresses the actual exposure. Deployment speed is part of the architectural argument. Static rules retain their role in the integrated stack. <sentence>The two layers work together, and the AI layer does not replace deterministic enforcement for known, structured scenarios.>
How to evaluate AI-native insider risk platforms: what the architectural argument means for vendor selection
Selecting an AI-native insider risk platform requires evaluating whether the architecture actually closes the three blind spots or whether it is a rule-based system with an AI feature bolted on. The key questions follow directly from the architectural argument. Does it assemble the behavioral narrative, or does it hand the analyst a queue? The investigation should arrive pre-built, because if the analyst must reconstruct context from separate systems, the MTTI gains disappear. A multi-month deployment creates a coverage gap that defeats the purpose.
Candor is an AI-native data loss prevention and insider risk platform built to address the full architectural gap. It understands both the data and the person: what information means, where it is going, who is interacting with it, and the surrounding pattern of activity across enterprise systems. The platform combines modern DLP controls, including protection against sensitive data leaks and shadow AI, with behavioral detection and investigation. It integrates content, destination, identity, role, and surrounding behavior into a single decision rather than treating them as separate signals. The platform deploys in days, on-premise or in the cloud, and its outputs are explainable and auditable, with the full story assembled for the analyst and defensible in HR and legal contexts.
Stellar Cyber takes an agentic SOC approach built on Open XDR, ingesting telemetry from any vendor's tools and applying AI detection across the full stack. Its platform deploys autonomous detection, correlation, and response agents operating across endpoints, networks, cloud, and identity systems, and it uses GraphML technology to connect related security events across the attack surface into unified incidents. The platform suits organizations seeking broad SOC automation across external and insider threat scenarios with a mixed existing security stack. Seceon's Open XDR platform applies AI and machine learning, behavioral analytics, and Dynamic Threat Modeling across hybrid, multi-cloud, OT, IoT, and edge environments. It is designed for continuous, autonomous detection-to-response with self-learning and self-tuning models, and it suits organizations with complex hybrid infrastructure requiring broad environment coverage beyond the enterprise endpoint and SaaS layer.
Corelight applies supervised and unsupervised machine learning to network telemetry, identifying both known threat patterns and novel anomalies that signature-based engines miss. It is particularly suited for network-layer detection of lateral movement, fileless attacks, and living-off-the-land techniques that leave no signature to match. Organizations evaluating Corelight for insider risk should assess how its network-layer visibility integrates with identity and endpoint behavioral data, since insider risk requires the full cross-system behavioral picture.