Is Replacing Legacy DLP With a Behavioral Insider Threat Platform Worth It
A behavioral platform closes detection gaps legacy DLP can't fix through configuration alone.
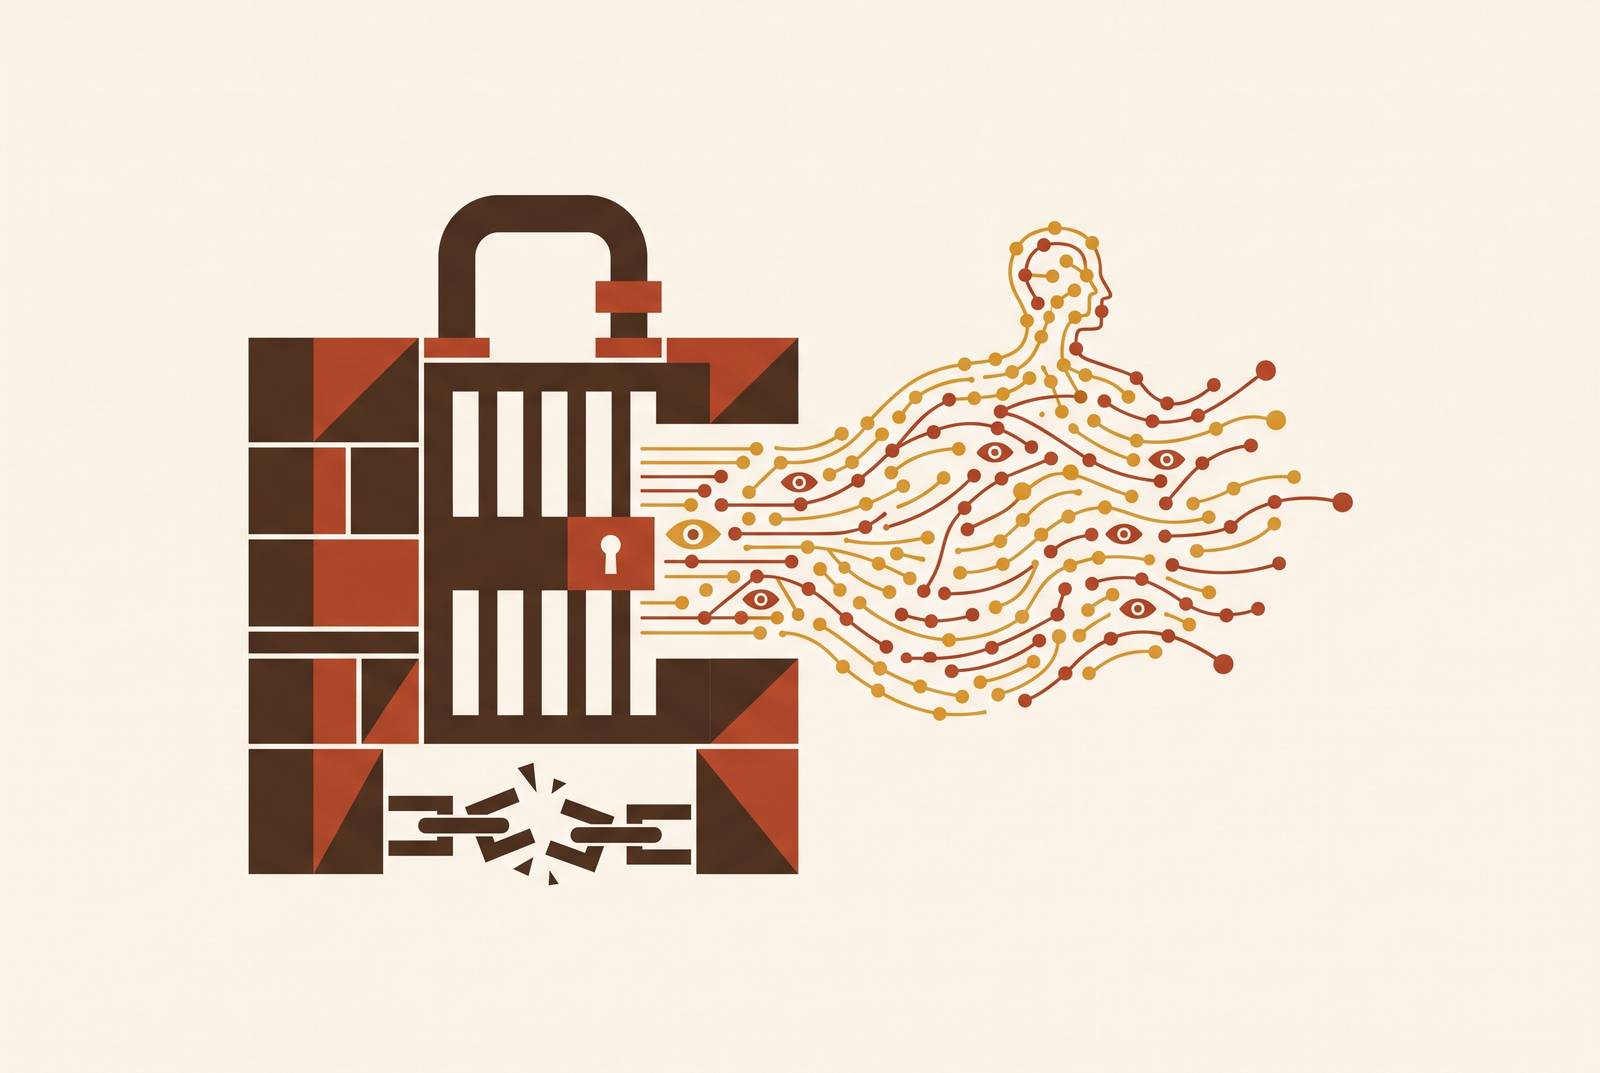
Legacy DLP is failing because it was built for a perimeter that no longer exists, and no amount of tuning restores a boundary that has already dissolved. The honest answer to whether a behavioral insider threat platform is worth the switch depends on one diagnostic question: is the current program missing threats because its rules need adjustment, or because the architecture itself has no way to see them? This piece lays out how to tell the difference, what the real-world incident record says about the gap, and what changes mechanically when an organization moves to a behavioral architecture.
Why legacy DLP no longer fits today's data environment
Legacy data loss prevention tools were engineered to watch defined boundaries: email leaving the network, files crossing a managed gateway, transfers off a corporate endpoint. The tool keeps watching the old boundary long after the data stopped respecting it.
The limit is architectural. Once data leaves the monitored environment, copied to a personal device, handed to a contractor, pasted into a browser-based AI tool, DLP's authority ends at that line. For organizations whose most sensitive material routinely flows to people they don't manage, that invisibility is a hole in the map.
A second structural gap sits underneath the first. Legacy DLP watches what data does, not who is moving it or why. Tuning the rules tighter doesn't fix this. What follows is whether a given program's shortcomings are things an administrator can fix with better configuration, or whether they're baked into what the tool was ever able to see.
Configuration problems versus structural ones in DLP programs
Before any practitioner decides to replace a platform, it helps to know which kind of problem they actually have. A configuration problem responds to tuning. A structural one doesn't, because the tool is working exactly as designed, and the design itself is what's holding the program back.
Configuration symptoms look like this: high false-positive rates on data types the policy already covers, rules that haven't caught up with a new SaaS tool the business adopted six months ago, coverage gaps on specific file types or upload destinations. None of them require a new architecture.
Structural symptoms look different, and they're harder to see coming. They include threats that moved entirely through access the user was authorized to have, leaving no event that any rule was built to catch. Some insider incidents only get discovered weeks or months after the fact, not while they're happening. They also include departing-employee risk, which only becomes obvious in hindsight, once someone reconstructs the timeline after the damage is done. They include data that left through a channel the tool was never pointed at. A clean alert queue doesn't mean a clean environment. It can just as easily mean the program has no way to see what already happened.
A useful question for any practitioner auditing their own setup: has the program ever caught an insider incident while it was in progress, or has it only ever confirmed one after the fact, once someone else noticed? That answer separates configuration problems from structural ones faster than any audit of policy rules can.
Three specific gaps sit outside what tuning can reach. The first is authorized-access blindness: when a legitimate user touches data they're allowed to touch and moves it through a channel they're allowed to use, no static rule has a reason to fire, because nothing about the action looks wrong on its face. The second is the non-corporate-account gap: employees pasting internal documents, source code, or strategic plans into public AI platforms operate entirely outside the boundary legacy DLP and traditional UEBA tools were built to watch. Neither category of tool was built with that surface in view. The third is the non-human identity gap: service accounts and AI agents now hold standing privilege and act on their own, and there's no human behavioral baseline to compare them against, which leaves static-rule tools with nothing to measure them by.
What real insider incidents reveal about the detection gap
The incidents that expose legacy DLP's ceiling are patterns that repeat across enough organizations to count as archetypes, and most insider risk programs will eventually run into some version of each one.
The first can be called the channel-pivot archetype, and Intel's experience with it is instructive. The tool did what it was built to do and still failed, because the threat didn't disappear when one channel closed. It pivoted to a second channel the tool had no visibility into. No amount of tuning stops a determined insider from finding the next open door once the first one shuts.
The second is the departure-window archetype. The notice period is the highest-risk stretch of the entire employee lifecycle, because access is still active, and nothing about using that access looks abnormal to a rule built to catch policy violations, not behavioral shifts.
The third is the collusive-insider archetype, visible in Coinbase's May 2025 incident, in which external attackers bribed support agents who then used their own legitimate access to pull customer data. A static rule has no way to anticipate that a credential's legitimate holder has been paid to misuse it.
In each case, the threat moved through authorized access, over an extended stretch of time, without ever tripping a content rule, which let it go undetected until long after the damage was done. That points to a specific conclusion about what detection actually needs to cover. The gap is in sequencing behavior across a user's timeline, so that a string of individually unremarkable actions can be read together as a pattern. Negligent insiders make up the largest share of incidents by volume, but the cases that expose real structural failure are the ones involving intent, where the tool had every chance to surface the pattern and didn't. The departure window concentrates this risk especially tightly: unusual download volumes from sensitive repositories, access to proprietary code at odd hours, and the sudden use of personal cloud storage are each unremarkable alone, but become meaningful once read in combination.
The two objections to replacement that practitioners should take seriously
The case for moving to a behavioral platform is strong, but two objections deserve real engagement, because practitioners who wave them off tend to rebuild the same problem at a more sophisticated layer.
The first objection: behavioral platforms can generate their own noise. If a platform scores every anomaly without sequencing those anomalies into a coherent story, it produces a different flavor of noise, not the absence of it. You shouldn't ask whether a behavioral tool generates signals at all. It's whether those signals have already been investigated and strung into a timeline before a human analyst ever sees them, because handing an analyst a fully assembled incident is a fundamentally different operational experience than handing them a raw anomaly score and asking them to make sense of it. Mean time to investigation matters as much as raw detection accuracy. A platform that flags the right event but leaves an analyst to piece the story together from scattered logs hasn't actually solved the problem it was bought to solve.
The second objection: governance has to come before tooling. Behavioral findings need cross-functional ownership, spanning security, HR, legal, and executive sponsorship, before anyone can act on them responsibly. CISA's January 2026 guidance for critical infrastructure organizations reflects this directly, describing actionable strategies for assembling a multi-disciplinary insider threat management team that combines physical security, cybersecurity, personnel awareness, and community partnerships. The governance overhead this requires is a real cost, but it's a sequencing question, not a reason to stay on a tool that structurally can't see the threats that matter. The practical path is to build the governance chassis in parallel with platform evaluation rather than waiting for one to finish before starting the other. The question that actually settles this, for any given organization, is whether its legacy DLP deployment is still contributing real signal, or whether it has become pure noise and operational overhead with no detection value left to preserve.
Architectural changes from a behavioral insider risk platform
The core shift is a move from content-matching at fixed boundaries to risk scoring across a full user timeline, and that's a difference in kind rather than a difference in degree.
Instead of static rules firing on individual events, behavioral platforms use machine learning to build a baseline of normal behavior for each user, then flag deviations from that baseline, and they automatically string related high-risk actions into a single risk-scored incident. A single anomalous action is prioritized as one signal in this system, instead of three disconnected alerts an analyst has to connect by hand.
Instead of watching data movement in isolation, these platforms correlate HR signals, an upcoming departure, a performance improvement plan, a role change, with access patterns, download volumes, and data-movement telemetry. Each of these signals can look ordinary on its own. Combined, they raise risk that no single-channel rule would catch. Instead of generating raw alerts and leaving analysts to reconstruct what happened, these platforms assemble the investigation before a human ever sees it, building a time-sequenced activity feed with forensic detail available on demand, covering what happened before, during, and after the event in question. Mean time to investigation moves toward zero because the investigation starts the moment the system flags something, rather than waiting in a queue for an available analyst.
Response also changes shape. Rather than a binary block-or-allow decision, these platforms support graduated enforcement, from real-time coaching nudges at the moment risk appears, to blocking a specific file from leaving, up to quarantining a device. That range lets the system step in without shutting down legitimate work, which a static rule could never tell apart from an actual threat.
Shadow AI is a clear example of the shift. Employees pasting internal documents, source code, or strategic plans into public AI tools represent a threat surface legacy DLP was never built to reach. Behavioral platforms extend coverage into that surface by governing whether sensitive content reaches a given destination, based on what the content is, who owns the account, and the context around the action. Behavioral insider threat platforms are purpose-built to close exactly this kind of architectural gap: they profile users across the entire enterprise stack rather than only at network boundaries, so threats moving through authorized access or through unmonitored channels become visible in places static rules were never positioned to look. Candor is one platform built around this approach.
Data lineage closes a related gap. Tracing where content originated, an HR export, a source-code repository, and applying policy based on whether the egress is corporate or personal, gives investigators an auditable record of what moved, where it went, who moved it, and how. That record turns investigations that used to be reconstruction exercises into something closer to a readable history. And because detection runs on behavior and context rather than pattern-matching against a regex, these platforms can surface risk around material that carries no label at all, so they protect exactly the unlabeled, high-value IP that content-matching rules were always going to miss.
Platforms that represent the behavioral insider risk architecture in practice
Evaluating vendors in this category means looking past feature lists to the underlying architecture: does the platform score behavior across a full timeline, or does it still fundamentally watch for rule violations with a behavioral layer bolted on top? The gaps between tools in this space tend to be structural choices about what each one was actually built to do, not cosmetic differences in dashboard design.
Candor Security is built as an AI-powered DLP and insider risk platform, and it aims to protect critical intellectual property by reading both the data in motion and the person behind it. It combines AI-driven DLP, including protection against sensitive data leaks and shadow AI use, with behavioral detection and investigation that spans enterprise systems, so it doesn't stop at a single egress point. The platform reads content, destination, identity, role, and the surrounding behavioral pattern as part of one decision, instead of treating each as a separate signal handled by a separate tool. Its shadow AI controls work by evaluating content, destination, account ownership, and context together, intervening before sensitive data actually leaves rather than relying on a blanket ban or settling for visibility without action. Candidate events are investigated by the system before they ever reach a human analyst's queue, which is meant to cut mean time to investigation rather than simply swap one kind of alert backlog for another. Detection decisions are built to be explainable and auditable rather than opaque, which matters directly for the cross-functional governance work, HR, legal, and security teams acting together, that has to happen before any behavioral finding turns into action. Deployment takes about a week, whether the environment is on-premise or cloud-based, so it avoids the months-long discovery phase that tends to stall legacy DLP rollouts before they produce any value. And because its detection logic isn't tied to labels, it can surface risk around the unlabeled IP that a classification-dependent tool would never flag.
If you're evaluating this space, weigh how fully each vendor has built the behavioral architecture described above, rather than how many features appear on a comparison sheet: a tool that scores isolated anomalies catches the next insider incident only after the fact, while one that sequences a full user timeline into a single investigable incident can catch it in progress.