On-Premise vs Cloud-Hosted Insider Threat Platform Deployment Tradeoffs
Architecture determines detection capability more than infrastructure choice alone.
For most enterprise software, the choice between cloud and on-premise deployment comes down to cost and scale. Insider threat detection doesn't work that way, because the deployment model itself decides what the platform can actually see. To detect insider risk, you need continuous, deep access to the behavioral record of every user across every system they touch, from email to cloud storage to the browser-based AI tools employees now use without asking anyone's permission. Candor is an AI-native behavioral DLP platform that profiles users across the enterprise stack to surface the patterns that separate real risk from routine activity, but it cannot deliver that fidelity if its deployment architecture cuts it off from the data sources that matter. For insider threat work, architecture is a detection problem first and an infrastructure problem second. Most organizations now run hybrid data estates, with sensitive information moving across on-premise systems, SaaS applications, cloud storage, and AI tools at the same time, so a platform that only reaches one segment of that environment starts with blind spots built into its design.
Deployment models: what they control and what they give up
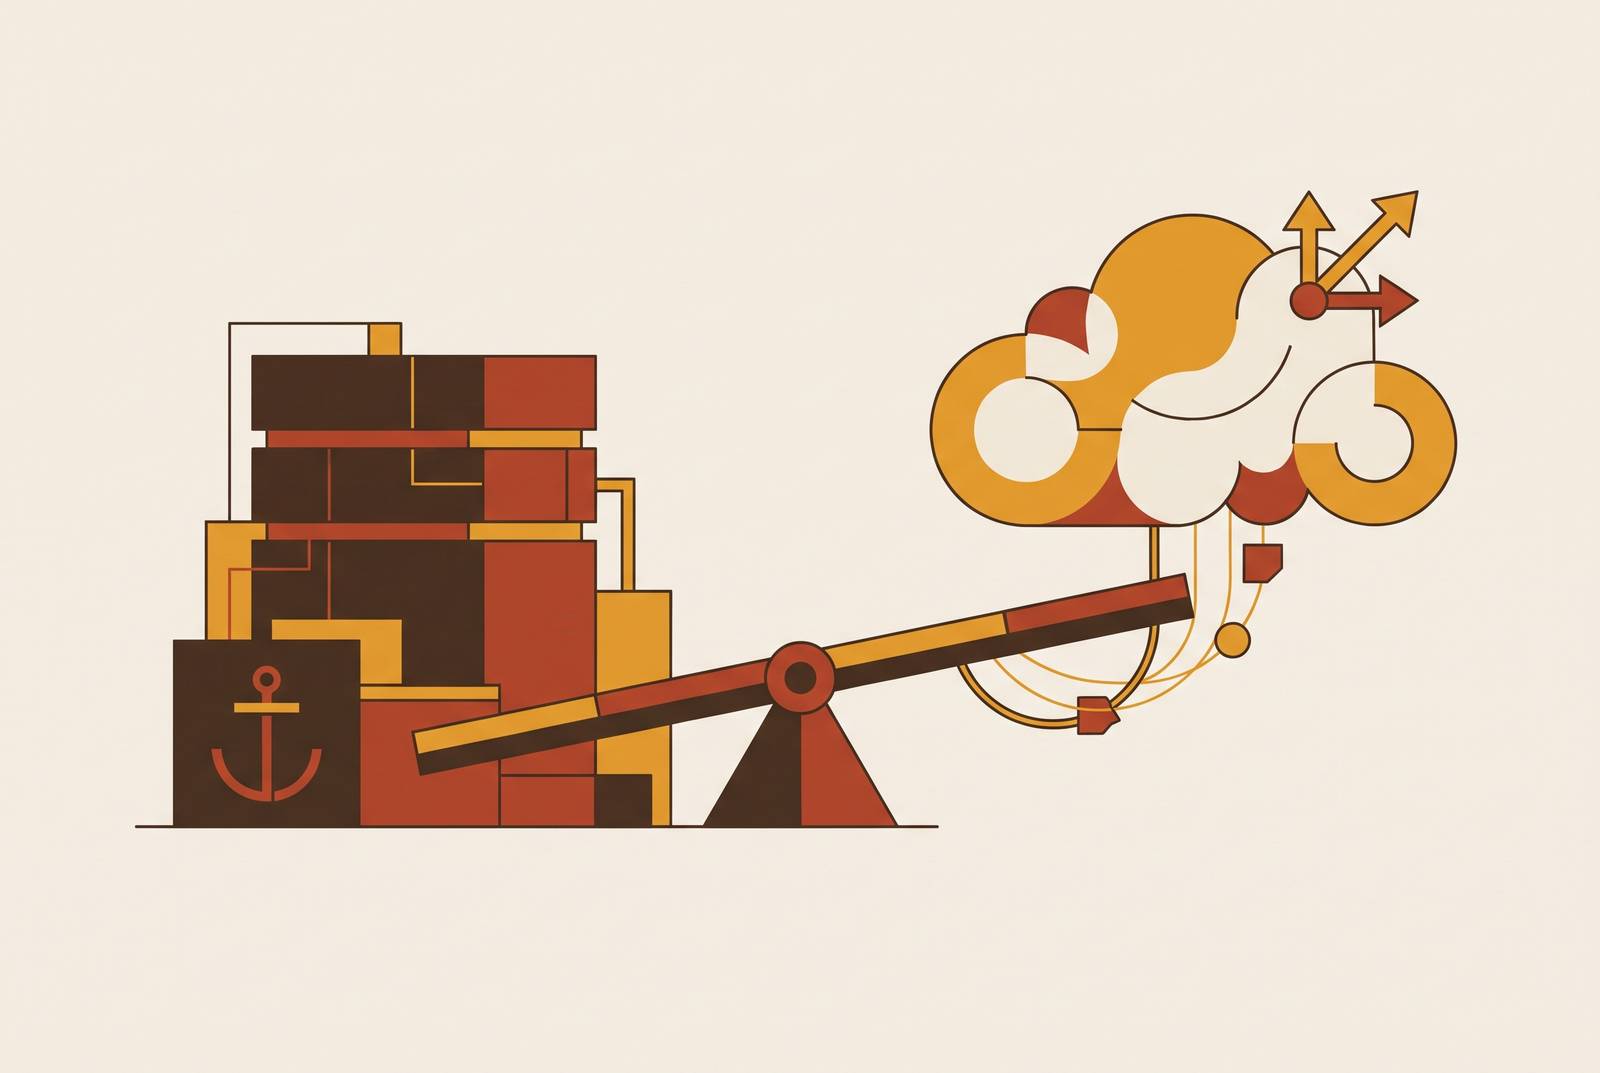
On-premise and cloud-hosted deployment split up security responsibility in different ways, and for insider risk, that split decides who owns the evidence chain when something goes wrong. On-premise deployment follows a dedicated, all-in model: the organization owns and runs everything, from the physical servers up through incident response. That ownership gives the security team the complete audit trail, which matters in forensic and litigation contexts where chain of custody gets contested in court. Full access to infrastructure metrics, logs, and diagnostic tools also supports deeper root-cause analysis, and because no data leaves the building, on-premise deployment avoids the multi-tenant exposure that comes with sharing cloud infrastructure with other customers. On-premise AI can give compliance teams a complete audit trail showing which model processed which data, when, and under what access controls, because the organization owns the entire stack top to bottom. Certain regulated data classes need exactly that level of control, and cloud environments cannot fully replicate it. The cost structure also tends to favor on-premise at high, sustained volumes. Lenovo's 2026 research found that on-premise AI reaches cost breakeven against cloud IaaS in under four months and delivers roughly an 8x cost advantage per million tokens at enterprise scale, a gap that matters for platforms running continuous behavioral analytics across large user populations. The tradeoff is time and labor: hardware procurement and configuration add weeks before a platform goes live, compared to cloud deployments that can run within hours, and every patch, update, and permission change requires internal IT to act on it.
Cloud-hosted deployment distributes responsibility differently. The shared responsibility model gives organizations automation and built-in security tooling, but it demands discipline when you configure it. Most of the security gaps in cloud deployments occur when teams misunderstand the boundary between what the provider secures and what the customer is responsible for, not because of any inherent weakness in the model itself. Cloud platforms update themselves, connect more readily to modern SaaS telemetry pipelines, and ask less of internal infrastructure teams, sparing lean security teams the work of maintaining a platform themselves. Cloud infrastructure also scales in minutes rather than weeks: a platform can expand to cover new user populations, new SaaS integrations, or new telemetry sources without a hardware procurement cycle standing in the way, which matters directly to insider risk programs that need to add a data source the moment a new exfiltration vector turns up. Cloud-hosted platforms, in this sense, update automatically and integrate readily with modern SaaS telemetry pipelines, scaling detection coverage in minutes when a new risk surface appears, a real advantage for programs that need to keep pace with an evolving threat picture. The cost of that convenience is that sensitive data moving to and through a multi-tenant cloud environment carries third-party access risk that on-premise deployment doesn't carry, and certain regulatory regimes, including some forms of government-controlled or classified data, may rule out cloud processing.
How cloud environments have changed the insider threat surface
Cloud infrastructure hasn't just changed where data lives. It has changed what a malicious insider can do, how quickly they can do it, and how easily the act can hide inside normal activity. In a cloud environment, an employee holding the right IAM permissions can write a short script that copies the entire contents of a sensitive S3 bucket or database to an external account in a matter of minutes. On-premise data theft was historically slower and bounded by network bandwidth and physical media, which gave defenders more time and more physical evidence to work with. Privilege creep makes the cloud version of this problem worse: employees change roles constantly in fast-moving tech organizations, but old permissions rarely get revoked when they move on, so a long-tenured employee can accumulate administrative rights that have nothing to do with their current job. Those accumulated rights look entirely legitimate to a rule-based detection system, because they are.
Infrastructure-as-Code introduces a sabotage vector that has no real on-premise equivalent. A single disgruntled DevOps engineer can insert a few malicious lines into a Terraform or CloudFormation script, sabotaging a production environment or planting a hidden backdoor, and that change can sit buried inside thousands of lines of legitimate code where no human reviewer is likely to catch it. The 2025 crypto exchange incident shows how this plays out at scale: overseas customer-support agents were recruited by outside criminals to abuse their legitimate access to support tools, exfiltrating data on a small subset of customers before the attackers demanded a ransom. The insider action in that case was indistinguishable from ordinary support-tool usage under any static rule set, because nothing about the access itself was unauthorized. Cloud environments compound all of this with fragmented logging spread across dozens of disparate services, so building a single, unified view of one person's activity across that sprawl becomes a serious operational problem in its own right, one the detection platform has to solve by aggregating across sources before it can reconstruct a coherent timeline.
The visibility problem both deployment models must solve first
The biggest failure mode in insider threat programs is analysts drowning in alerts that were never real risks, while the activity that actually mattered looked identical to routine work and got buried in the noise. Legacy DLP built on static rules can report that a file moved, but judging whether that file should have moved in the first place is beyond it. That gap between a policy violation and a genuine risk is where most insider threat programs collapse under the sheer volume of alerts: Vertosoft found that 92% of DLP alerts are either false positives or simply ignored. The 2026 SANS SOC Survey backs this up at the operational level: it finds that a lack of enterprise-wide visibility is the single biggest barrier to effective SOC operations, ranked above both staffing shortages and automation gaps. Tool sprawl makes the problem worse rather than better. Vectra AI's 2026 research found that most organizations run more than ten separate detection and response tools, with a large share running more than twenty, and each tool generates its own alert stream with no shared behavioral context connecting them.
Two cases show what this costs in practice. Former Intel employee Jinfeng Luo downloaded a large volume of sensitive files shortly before he was terminated. Intel's DLP blocked one attempt to move the files to an external hard drive, but five days later, Luo just used a personal NAS device to complete the transfer. A unified timeline tracking his behavior across both attempts would have surfaced the pattern immediately, but a rule-based point solution, built to catch one channel at a time, had no way to connect the two events. A banking incident tells a similar story from the other direction: a former FinWise Bank employee accessed records belonging to roughly 689,000 customers using retained access on May 31, 2024, and the breach wasn't discovered until June 18, 2025, over a year later. No single system held the full behavioral record spanning the employee's tenure and departure, so the access sat there, undetected, for more than twelve months. Solving this requires evaluating content, destination, identity, role, and surrounding behavior together in one decision, not as five separate alerts from five separate tools, and that requirement shapes which deployment architectures are even viable before anyone gets to weighing preferences.
Why behavioral, AI-driven detection changes the deployment architecture's requirements
Behavioral DLP asks a different question than legacy tooling ever asked. Instead of checking whether an action violated policy X, it asks whether the action is normal for this specific user, in this context, at this time. Answering that question requires continuous access to a user's full historical record across every system they touch, and that requirement applies differently depending on the deployment model underneath it. Traditional DLP runs a substantial false positive rate in enterprise deployments, but AI-driven behavioral detection produces meaningfully lower rates that keep improving as the model sees more data. The practical difference appears in analyst workload: fewer wasted hours chasing noise, and a higher proportion of real risk surfacing instead of getting buried under false alarms. The IBM 2025 Cost of a Data Breach Report found that organizations using AI and automation extensively cut their average time to identify and contain a breach substantially. Mean time to investigation is the metric that matters here: when investigations consistently run long, it means the alert itself isn't carrying enough context, and it needs to be enriched with entity timelines, peer comparison, and historical risk scoring before an analyst can act on it with any confidence.
Shadow AI has emerged as its own fast-growing exfiltration surface. The same IBM report found that breach costs rose substantially at organizations with a high level of shadow AI use, and that nearly every organization hit by an AI-related security incident lacked proper access controls over the AI tools involved. That finding carries a direct architectural consequence. A behavioral platform has to ingest telemetry continuously, update its models as new behavior appears, and, where shadow AI is concerned, intercept data before it reaches an unmanaged destination. Cloud-hosted platforms can push out model updates and add new SaaS connectors faster, because no hardware cycle or IT-managed rollout stands between the vendor and the customer. On-premise platforms give up some of that update speed, but they can process the most sensitive behavioral signals without the data ever crossing the organization's boundary. Gartner's 2025 Market Guide on adaptive, risk-based DLP points toward where detection is headed, but it stops short of naming a formal category for agentic approaches. Neither deployment model wins this tradeoff. A security leader has to weigh update velocity against data containment according to their own threat profile, not according to which model sounds more modern on paper.
Regulatory and data sovereignty requirements that can force the deployment decision before any tradeoff analysis begins
For a meaningful share of organizations, the regulatory environment settles the deployment choice before any tradeoff analysis can even start. If sensitive data falls into certain classifications, jurisdictions, or industry regimes, it must be processed inside boundaries that cloud environments can't satisfy, no matter how the vendor configures its controls. Regulated industries and government contractors with strict data-handling requirements are better served by on-premise's dedicated, all-in security model. ITAR-controlled data, certain classified government work, and some financial datasets carry handling requirements, so they rule out multi-tenant cloud processing from the outset. Air-gapped environments take this further: for organizations that can't permit internet connectivity at all, including certain government facilities, defense contractors, and critical infrastructure operators, cloud deployment is an architectural impossibility given the environment's own constraints, not a tradeoff worth weighing.
Federal agencies handling classified or controlled unclassified information face a related constraint. They may need to process that data within specific, defined security boundaries, and government-authorized cloud services that meet strict compliance certifications can satisfy many of those requirements, but certain classifications and data types still call for on-premises processing no matter how you configure the cloud option. On-premise deployment gives the organization full custody of the evidence chain in these situations, which matters where forensic integrity and chain-of-custody audits are on the line, and it supports deeper root-cause analysis across infrastructure logs without the multi-tenant exposure that cloud platforms carry by design. If you operate under these constraints, you gain little from running a detailed tradeoff analysis between cloud convenience and on-premise control. The regulatory floor has already made the decision, and the work that remains is building the most capable detection architecture within the boundary that floor defines.